


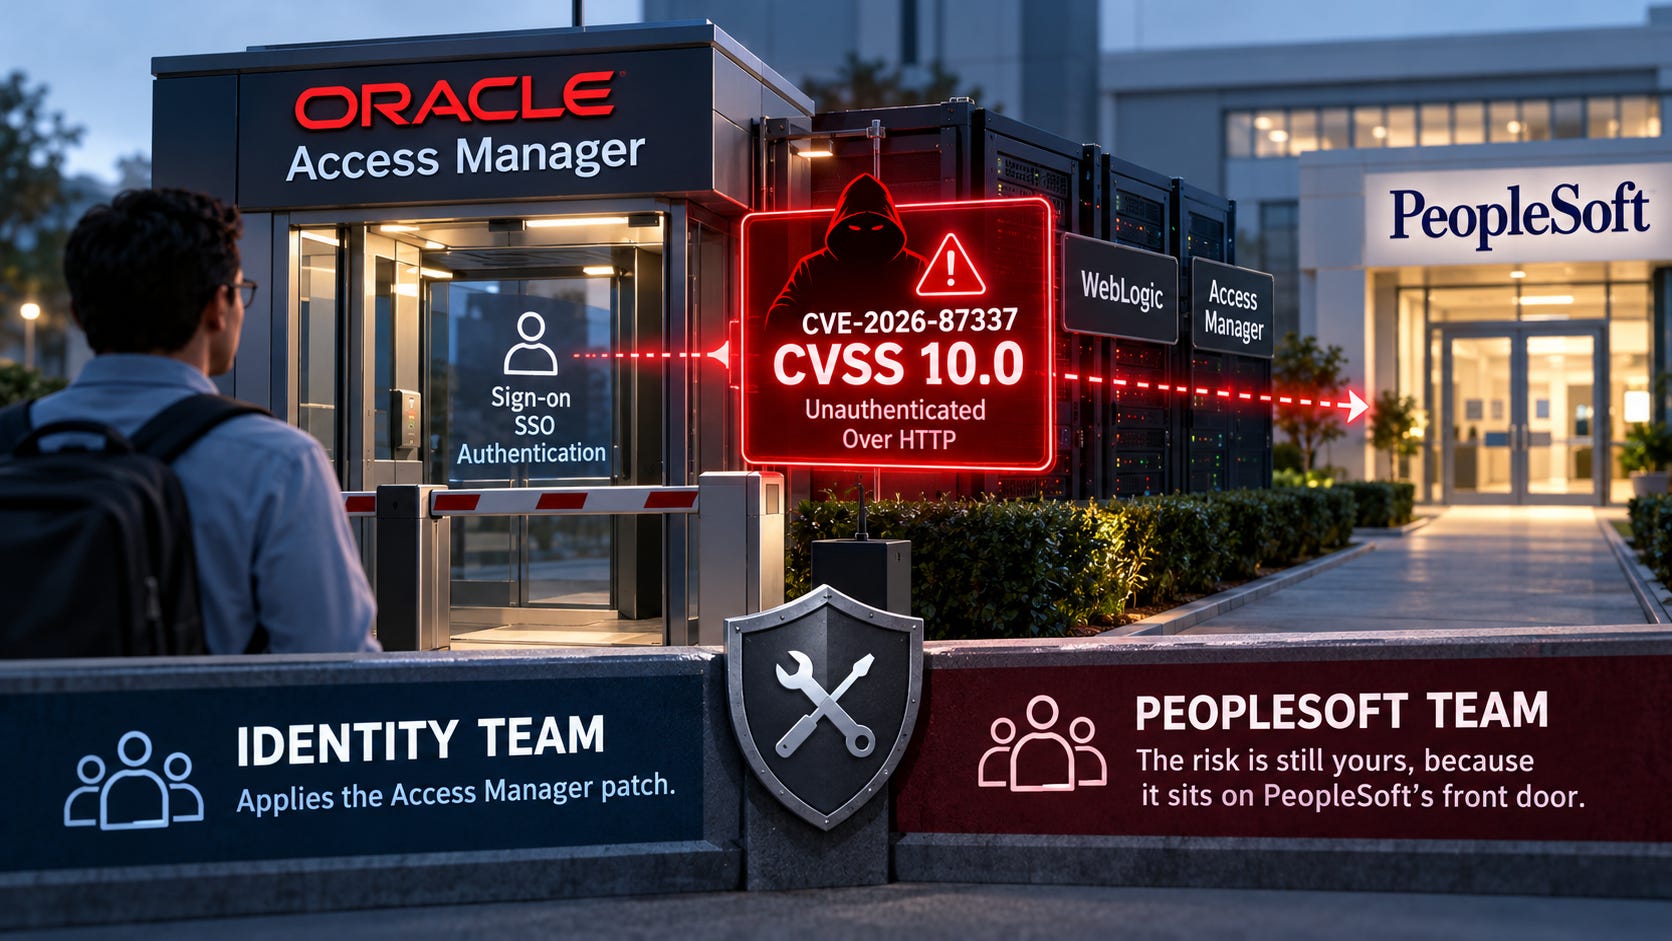
The short answer: Both, and that’s the trap. The identity team owns applying the Oracle Access Manager patch, but if Access Manager decides who gets into PIA, an unpatched Access Manager is a PeopleSoft exposure. Put it on your PeopleSoft CPU tracker with a named owner and a date, even though somebody else applies it.
What changed
Oracle’s October 2026 Critical Patch Update, published October 20, includes CVE-2026-87337 in the Oracle Access Manager Authentication Engine. It scores 10.0, it’s reachable over HTTP, and it needs no credentials. Oracle lists the affected versions as 12.2.1.4.0 and 14.1.2.1.0. The same component carries CVE-2026-87251, a 9.8 over SAML, on the same versions. Oracle Identity Manager adds an unauthenticated 9.8 over T3/IIOP (CVE-2026-91408).
None of that shows up in the PeopleSoft risk matrix. PeopleSoft’s own rows top out at 9.8. That’s why this one is easy to miss: the scariest score touching your PeopleSoft sign-on sits in the Fusion Middleware matrix, under a product your team may not patch.
The patch path splits the same way. The Middleware DPK covers Java, WebLogic, Tuxedo and the Oracle Database Client, which are the components Oracle lists for the Builder. Access Manager isn’t one of them. A PeopleSoft team can apply every Middleware DPK on schedule and still leave the sign-on tier untouched.
Waratek’s October analysis, a vendor piece, puts it plainly: Access Manager fronts single sign-on, so exposure extends to the applications it protects. Neither Fortra nor Waratek had seen public exploitation of the newly fixed flaws as of October 21. That’s a reason to schedule the fix this week, not a reason to wait.
What to do, in order
Draw the sign-on path. List every component a user’s request passes through before it reaches PIA: load balancer, proxy, Access Manager agent, Access Manager server, and the WebLogic it runs on. Write down the version of each one.
Match versions to the advisory. If Access Manager is 12.2.1.4.0 or 14.1.2.1.0, both Access Manager CVEs apply. If it’s a version Oracle doesn’t list, find out whether that’s because it isn’t affected or because it’s no longer supported. Those two answers lead to very different conversations.
Get a date from the identity team, in writing. Use Oracle’s patch availability documentation for the October CPU to identify the Access Manager patch. Patch the WebLogic underneath it too, since the October WebLogic 9.8s cover 12.2.1.4.0 through 15.1.1.0.0.
Cut exposure while you wait. Make sure Access Manager and WebLogic admin consoles aren’t reachable from the internet, and restrict T3/IIOP to the hosts that need it. That’s a stopgap and should be logged as one, with an end date.
Regression-test sign-on in non-prod. Test login, logout, session timeout, deep links into PIA, and any integration that authenticates through the same tier. When a sign-on patch breaks something, the help desk usually hears about it before you do.
Close it on the PeopleSoft tracker. Record it as done only when production is patched and someone has confirmed the version.
My read: PeopleTools 8.63 adds native SAML 2.0 and TOTP sign-on options, now available on-prem. That may be worth a look later. It doesn’t help with October. Don’t let “we might move off Access Manager” become the reason it isn’t patched.
Who owns it
Identity or middleware team: applies the Access Manager and Identity Manager patches and the WebLogic underneath them.
PeopleSoft technical lead: keeps the sign-on tier on the PeopleSoft CPU tracker and owns the regression test.
Security lead: approves any temporary exposure controls and any delay, in writing, with an end date.
CIO or IT director: makes sure the CPU tracker covers every layer a PeopleSoft request touches, not just the risk matrix with PeopleSoft in its name.
For leaders, in one line: If it decides who gets into PeopleSoft, it’s on the PeopleSoft patch list, no matter whose team applies it.
Got a PeopleSoft question? Reply to this email or leave a comment. I’ll pick one for a future Q&A and answer it straight.
Subscribe at peoplesoftcloud.com.
Sources
🔗 Oracle Critical Patch Update Advisory – October 2026 (Oracle, Oct 20, 2026) https://www.oracle.com/security-alerts/cpuoct2026.html
🔗 Middleware DPK Enablement Patches Now Available (Oracle / Dan Iverson, Oct 9, 2026) https://blogs.oracle.com/peoplesoft/middleware-dpk-enablement-patches-now-available
🔗 October 2026 Oracle Critical Patch Update Analysis (Fortra, Oct 21, 2026) https://www.fortra.com/blog/october-2026-oracle-critical-patch-update-analysis
🔗 Oracle Releases the October 2026 Critical Patch Update (Waratek, Oct 21, 2026) https://waratek.com/news/oracle-releases-the-october-2026-critical-patch-update/
🔗 PeopleTools 8.63 Is Now Available for On-Premises Installation (Oracle / Sasank Vemana, Oct 20, 2026) https://blogs.oracle.com/peoplesoft/peopletools-8-63-is-now-available-for-on-premises-installation